Introduction
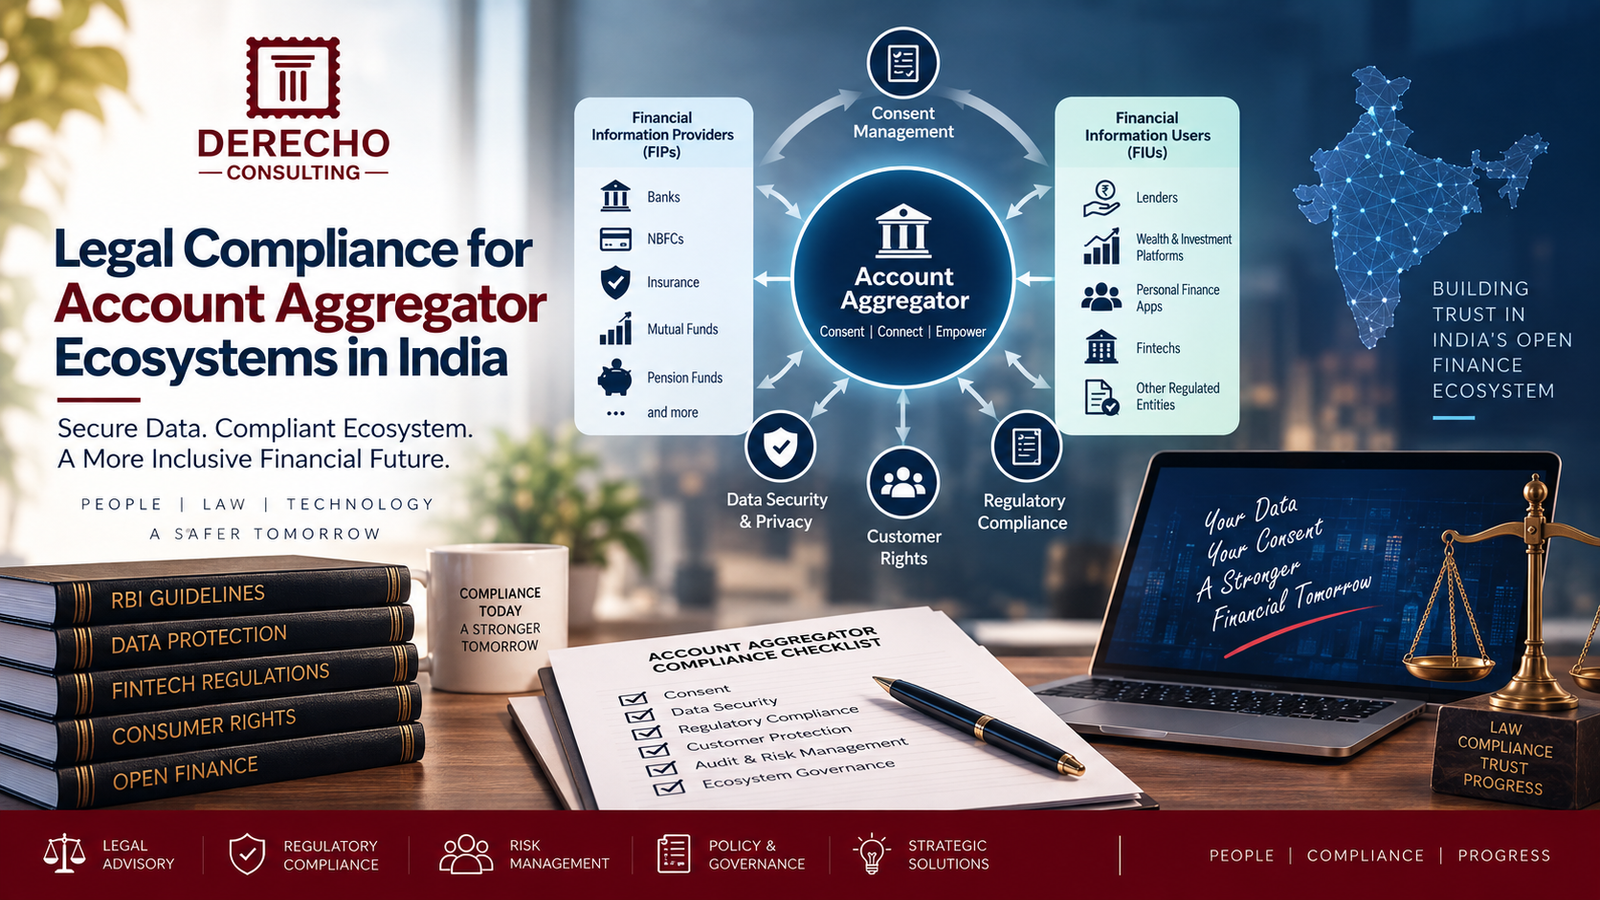
Account Aggregator Compliance is becoming increasingly important as India’s Account Aggregator ecosystem enables customers to share financial information electronically, securely, and with their explicit consent. Account Aggregators (AAs) act as consent managers and facilitate the movement of financial information between Financial Information Providers (FIPs) and Financial Information Users (FIUs).
The Reserve Bank of India’s Master Direction – Non-Banking Financial Company – Account Aggregator (Reserve Bank) Directions, 2016, currently listed by RBI as updated through 6 September 2024, establishes the regulatory framework for NBFC-Account Aggregators. The framework requires an AA to obtain explicit customer consent, manage consent artefacts, protect customer information, and securely facilitate financial-data flows.
The AA ecosystem is also supported by technical specifications developed by ReBIT, covering areas such as account discovery and linking, consent flows, financial-information transfer, notifications, and monitoring. RBI has also required relevant participants to adopt these technical specifications as updated from time to time.
A significant 2026 development is the ReBIT standard to enhance customer protection and user experience in the Account Aggregator framework. Published on 30 April 2026, the standard covers customer onboarding, consent management, user experience, and technical/security integration. NBFC-AAs and FI-Us are required to implement the standard by 31 October 2026.
This guide explains Account Aggregator Compliance in India, including registration, consent management, FIP and FIU responsibilities, data security, customer rights, technical standards, grievance redressal, third-party risks, audit requirements, and important 2026 compliance considerations.
Why Account Aggregator Compliance Matters
The Account Aggregator framework involves the transfer of financial information between multiple regulated entities and technology systems. Because financial information moves only through authorised and consent-based processes, strong compliance and security controls are essential.
Understanding Account Aggregator Compliance can help businesses:
- Meet applicable RBI requirements.
- Establish effective consent-management processes.
- Protect customer financial information.
- Maintain secure data flows.
- Clarify FIP and FIU responsibilities.
- Strengthen customer authentication.
- Maintain appropriate audit trails.
- Manage technology and integration risks.
- Improve customer transparency.
- Prepare for changing AA technical standards.
RBI’s framework specifically requires customer information to be retrieved, shared, or transferred only with the customer’s explicit consent, and requires AAs to provide customers with functionality to revoke consent.
Key Areas of Account Aggregator Compliance
1. RBI Registration and Regulatory Structure
An entity carrying on the business of an Account Aggregator generally needs to operate within the RBI’s prescribed regulatory framework.
The RBI Directions state that:
- Only a company can undertake the business of an Account Aggregator.
- An applicable company cannot commence or carry on AA business without obtaining a Certificate of Registration from RBI.
- NBFC-AAs remain in the Base Layer under the RBI’s scale-based regulatory structure.
- The AA framework is primarily focused on facilitating consent-based financial-information sharing.
Businesses considering the AA model should therefore assess their regulatory status and eligibility before beginning operations.
2. Consent Management
Consent is at the centre of Account Aggregator Compliance.
An AA must not retrieve, share, or transfer financial information without the customer’s explicit consent.
The consent framework includes:
- Customer identity.
- Nature of financial information requested.
- Purpose of collection.
- Identity of information recipients.
- Notification address.
- Consent creation date.
- Consent expiry date.
- AA identity and signature or digital signature.
- Ability to revoke consent.
The RBI Directions require consent to be managed through a standardised consent artefact and require electronic consent artefacts to be capable of being logged, audited, and verified.
3. Customer Onboarding and Account Linking
Customers must be able to securely discover and link relevant accounts within the AA ecosystem.
The technical framework includes account discovery and linking processes between participating entities.
Businesses should consider:
- Customer identification.
- Account discovery.
- Account linking.
- Account delinking.
- Authentication.
- Clear consent presentation.
- Error handling.
- Customer notifications.
In 2026, the new ReBIT baseline standard specifically addresses customer onboarding, account discovery, and linking as one of its four major areas.
4. Financial Information Provider Responsibilities
Financial Information Providers hold financial information and make that information available through the AA ecosystem when a valid consent artefact is presented.
The RBI framework requires FIPs to:
- Verify consent validity.
- Verify applicable dates and usage.
- Verify the AA credentials.
- Digitally sign financial information.
- Securely transmit information.
- Maintain logs of information-sharing requests and actions.
FIPs should therefore maintain appropriate technology, authentication, logging, and security controls.
5. Financial Information User Responsibilities
Financial Information Users receive customer financial information through the AA ecosystem for authorised purposes.
The framework requires an AA to verify the FIU’s identity before securely transferring information and restricts use or disclosure of information to what is specified in the consent artefact.
FIUs should therefore ensure that:
- The intended purpose is clearly defined.
- Data is used only for authorised purposes.
- Internal access is controlled.
- Data-handling procedures are documented.
- Consent records are maintained.
- Information is not used beyond the permitted scope.
6. Data Security and Privacy
The AA ecosystem depends on secure transfer of financial information between systems.
RBI requires AAs to implement appropriate IT frameworks and safeguards against:
- Unauthorised access.
- Alteration.
- Destruction.
- Disclosure.
- Dissemination of records and data.
The Directions also prohibit AAs from requesting or storing customer credentials such as passwords and PINs used for accessing financial information providers. Access must be based on consent-based authorisation.
Businesses should therefore establish strong data-security and privacy controls throughout the AA lifecycle.
7. Customer Financial Information Storage
A distinctive feature of the AA framework is that financial information accessed by the AA from an FIP should not reside with the AA.
The RBI Directions expressly state that financial information accessed by an AA from an FIP should not reside with the AA, while the customer should be able to access records of consents granted and the FIUs with which information has been shared.
This structure reinforces the consent-based and data-blind nature of the AA model.
8. Technical Specifications and Secure Integration
Account Aggregator participants rely on standardised APIs and technical specifications to enable secure data exchange.
ReBIT’s technical specifications cover:
- Account discovery and linking.
- Consent requests.
- Consent-handle management.
- Financial-information requests and retrieval.
- Notifications.
- Monitoring and heartbeat mechanisms.
RBI has also directed applicable participants to adopt the technical specifications published by ReBIT and updated from time to time.
Organisations should therefore maintain controlled API integration, authentication, monitoring, and testing procedures.
9. Customer Rights and Consent Revocation
Customers have important control rights within the AA framework.
An AA must provide functionality that enables customers to:
- View their consent records.
- See the FIUs with which information has been shared.
- Revoke consent.
- Revoke consent for parts of the information where applicable.
The framework also states that an AA should not access or use customer information except for carrying out the account-aggregation service explicitly requested by the customer.
Clear consent visibility and revocation mechanisms are therefore central to effective compliance.
10. Customer Grievance Redressal
A compliant AA must maintain a structured customer-grievance framework.
The RBI Directions require:
- A Board-approved grievance policy.
- A dedicated grievance-handling setup.
- A designated Grievance Redressal Officer.
- Prominent display of grievance-contact information.
- Complaint resolution within the period specified in the policy, but not beyond one month from receipt.
- Information to customers about escalation to RBI where a complaint is not resolved within one month.
Businesses should therefore ensure that their grievance mechanisms are documented, accessible, and appropriately staffed.
11. Information System Audit and Business Continuity
Technology risk is a major component of Account Aggregator Compliance because the AA model is entirely IT-driven.
The RBI framework requires appropriate measures for:
- Disaster risk management.
- Business continuity.
- IT safeguards.
- Information-system audit.
The Directions require internal systems and processes to undergo an information-system audit at least once every two years by a CISA-certified external auditor, with the prescribed report-submission requirement.
A strong audit and continuity framework can help organisations maintain ecosystem resilience.
12. 2026 Customer Protection and User Experience Standards
A major 2026 development is ReBIT’s new baseline standard designed to enhance customer protection and user experience.
The standard covers four broad areas:
- Customer onboarding, account discovery, and linking.
- Consent management.
- User experience.
- Technical, security, and integration requirements.
It includes measures such as clearer consent fields, improved customer control over consent operations, timely notifications, two-factor authentication, SIM/device binding, and secure integration between AA and FIU applications. NBFC-AAs and FI-Us are required to adopt the standard by 31 October 2026.
Businesses should therefore treat 2026 as an important implementation year for improving customer-facing and technical AA controls.
Common Account Aggregator Compliance Risks
Businesses participating in the AA ecosystem may face Account Aggregator Compliance risks due to:
- Invalid or incomplete consent.
- Poor consent presentation.
- Inadequate consent-revocation functionality.
- Weak customer authentication.
- Insecure API integrations.
- Unauthorised use of financial information.
- Poor access controls.
- Inadequate logging.
- Failure to follow technical specifications.
- Unclear FIP/FIU responsibilities.
- Weak third-party technology controls.
- Inadequate grievance mechanisms.
- Insufficient cybersecurity controls.
- Weak business-continuity arrangements.
- Delayed implementation of updated technical standards.
- Inadequate audit and compliance documentation.
These weaknesses can create privacy, cybersecurity, regulatory, operational, and reputational risks.
Best Practices for Account Aggregator Compliance
Businesses participating in the AA ecosystem should consider the following practices:
- Maintain clear consent-management procedures.
- Make consent information easy for customers to understand.
- Implement reliable consent-revocation mechanisms.
- Use strong customer authentication.
- Follow applicable RBI and ReBIT technical specifications.
- Secure APIs and system integrations.
- Maintain detailed information-sharing logs.
- Restrict internal access to authorised personnel.
- Ensure information is used only for permitted purposes.
- Conduct regular technology and security assessments.
- Maintain business-continuity and disaster-recovery plans.
- Conduct required information-system audits.
- Review FIP/FIU and vendor agreements.
- Maintain a Board-approved grievance policy where applicable.
- Track regulatory and technical updates.
- Document implementation of new AA standards.
A coordinated legal, compliance, technology, privacy, and cybersecurity approach can help organisations maintain effective Account Aggregator Compliance.
2026 Account Aggregator Compliance Considerations
Account Aggregator Compliance is particularly important in 2026 as the AA ecosystem continues to expand and customer-protection and technical standards become more detailed.
The RBI framework currently available is the NBFC-AA Directions, 2016 updated through 6 September 2024, while the ecosystem’s technical standards continue to evolve through ReBIT.
A key 2026 development is the ReBIT standard published on 30 April 2026, which requires NBFC-AAs and FI-Us to implement enhanced customer-protection and user-experience measures by 31 October 2026.
Businesses should therefore pay particular attention to:
- Enhanced consent-management controls.
- Clear and legible consent fields.
- Customer control over consent operations.
- Two-factor authentication.
- SIM and device binding.
- Secure AA-FIU integration.
- Account discovery and linking.
- Timely customer notifications.
- Updated API specifications.
- Technical-security testing.
- Audit and compliance documentation.
- FIP and FIU governance.
- Third-party technology risk.
RBI’s framework has also continued to expand the ecosystem by recognising additional Financial Information Providers over time, including the inclusion of Central Recordkeeping Agencies for the NPS architecture in 2023 and other regulated financial information sources.
Businesses should therefore keep their AA implementation aligned with the latest RBI and ReBIT requirements rather than relying only on older implementation documentation.
How Derecho Consulting Can Help
Derecho Consulting can help businesses manage Account Aggregator Compliance through regulatory assessments, AA-framework reviews, consent-management assessments, FIP/FIU compliance reviews, technology-contract analysis, data-protection assessments, cybersecurity governance, grievance-process reviews, vendor due diligence, and regulatory-change monitoring.
A proactive approach can help businesses:
- Assess applicable RBI requirements.
- Review consent-management processes.
- Evaluate FIP and FIU responsibilities.
- Review contracts and technology arrangements.
- Strengthen data-security controls.
- Assess API and third-party integration risks.
- Review customer-grievance mechanisms.
- Prepare for new technical standards.
- Maintain compliance documentation.
- Identify regulatory gaps before they become operational problems.
Derecho Consulting can also assist organisations with periodic reviews of their AA compliance framework as RBI and ReBIT requirements continue to evolve.
Conclusion
Legal Compliance for Account Aggregator Ecosystems in India requires businesses to combine regulatory compliance, customer-consent management, secure technology infrastructure, data governance, and operational controls. The RBI’s framework places explicit consent, secure financial-information flows, customer rights, data security, auditability, and grievance redressal at the centre of the AA model.
The 2026 ReBIT standard adds an important customer-protection and user-experience layer, with NBFC-AAs and FI-Us required to implement the specified baseline standard by 31 October 2026.
By maintaining strong consent mechanisms, secure integrations, appropriate customer controls, effective governance, detailed records, and updated technical standards, participants can reduce regulatory and operational risks.
A proactive and well-documented approach to Account Aggregator Compliance can help businesses protect customer financial information, strengthen trust, meet applicable regulatory expectations, and participate more effectively in India’s evolving open-finance ecosystem.